ACL Explorer
Audit tool — see exactly what any user can access and why
Without this app, debugging permissions is guesswork
A user reports they can't access a document. You know they're in a group, the group is linked to a role, and the role has some ACLs configured somewhere — but tracing the full chain manually means navigating through Users, Groups, Roles, and ACL tabs one by one.
Mayan has no built-in way to answer "what can this user actually do?" in a single view.
What ACL Explorer shows you
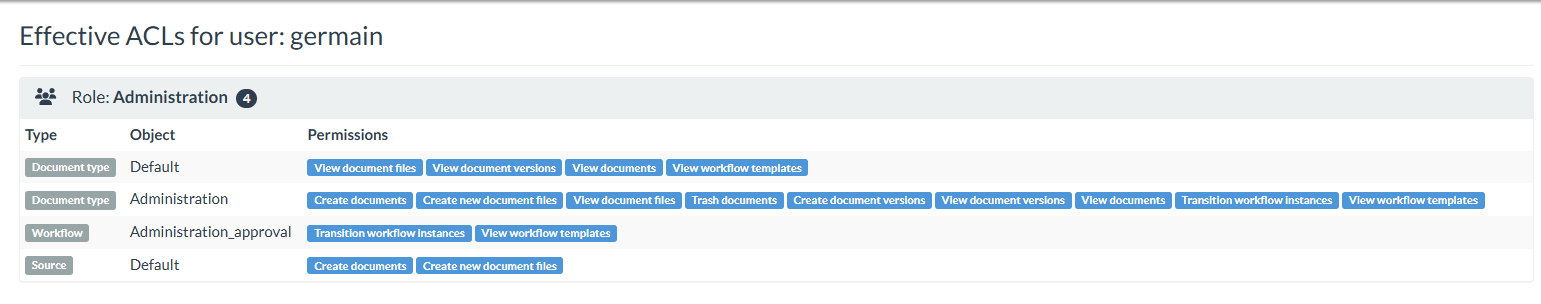
- Complete effective permissions, per user. Open any user's profile and see every ACL grant they hold — consolidated from all their roles — in a single table. No more tab-hopping.
- Organized by role. Each role the user belongs to is listed as a collapsible group, with the objects and permissions it grants clearly laid out.
- Object-level detail. Each entry shows the exact object (document type, cabinet, workflow…) and the specific permissions granted on it — not just "has access to something."
- Immediate diagnosis. A user can't see a cabinet? Open ACL Explorer, find the cabinet in their permission list — or confirm it's missing and know exactly which role to fix.
- Access-controlled. Only users with the View user permission can open another user's ACL view — the tool respects your existing Mayan security model.
Ideal for: Mayan administrators managing multiple roles and complex permission structures — anyone who has ever spent 20 minutes figuring out why a user can or cannot see something.
Private repo access included
Updates included
Compatible Mayan 4.x